2-Factor Authentication
The second step in your defence against hackers. Learn how 2FA works, why it matters, and how newer options like passkeys and security keys fit into account security.
Editor’s note: This article was originally published in August 2020 and updated in August 2026.
In the last article in this series, we taught you how important it was to have strong, unique passwords for each of your online services.
Now, we’re going to take things one step further. For your really important accounts, we are going to get you set up with something called “2-Factor Authentication” (2FA).
You will learn:
- How 2FA works
- Why it’s important to use 2FA
- Different kinds of 2FA, their pros and cons
- How to set up 2FA on your accounts
- How passkeys and security keys protect against phishing
Let’s get started.
Follow along with these resources
What is 2-Factor Authentication?
Two-factor authentication is an authentication method that requires two pieces of evidence to prove you are the person who should be granted access to an account. Typically, these two factors are considered to be “something you know” (your password, a PIN) and “something you have” (a smartphone, a hardware token, a security key).
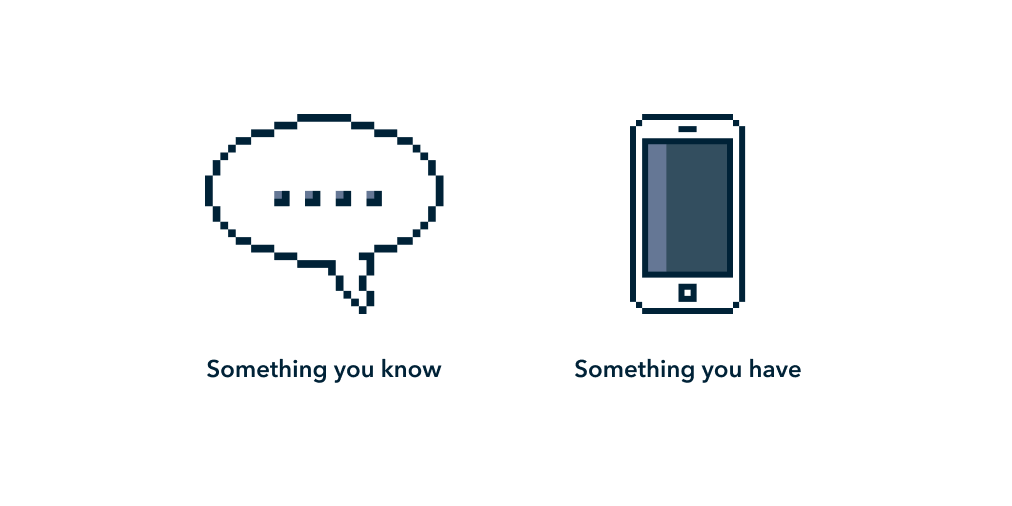
Fun fact: you already use 2FA every time you visit a bank ATM to withdraw some cash. The debit card in your hand counts as “something you have” and your private PIN is “something you know.” An ATM prompts you for each of these in succession and then, should you pass the test, grants you access to your funds.
There’s also a third category of authentication evidence: “something you are,” such as a fingerprint or facial recognition. Modern sign-in methods can combine these categories. For example, a passkey may use your device and your fingerprint, face, or device PIN to approve a sign-in.
With online accounts, two-factor authentication works in a similar way:
- Enter your username and password.
- The service will ask you to authenticate with a second factor by sharing a temporary number, plugging in a security key or typing a backup code.
- You will then be granted access to your account as usual.
Why is 2FA important?
2FA offers an extra layer of security for your accounts. This is especially important for your most important accounts like email, social media, online banking, digital currency platforms, cloud file storage, and password managers.
If, for example, someone takes over your primary email account, they can reset your other account passwords. They might read and delete your emails; make online purchases in your name; steal your digital currency; blackmail or extort you; impersonate you; delete your files and backups; and, if you’re not able to regain access, lock you out of your important accounts forever.
A second factor helps protect against stolen or reused passwords, but it does not eliminate every security risk. Phishing, malware, unsafe recovery settings, and stolen devices can still put an account at risk.
Isn’t a password enough to protect me?
While choosing a great password is a big part of security, there are still a number of ways that bad actors can get hold of your credentials:
- Malware on your device
- Cameras that record your keystrokes
- An acquaintance or onlooker peering over your shoulder
- Man-in-the-middle attacks
- Credential stuffing
- Brute-force attacks
- Large-scale data breaches of organizations
A password is still important, but it works best as part of a broader security setup. Use a unique password for every account, protect the email address that can reset your other accounts, and add the strongest additional sign-in method the account supports.
Digital currency users should take special care
Financial accounts can be attractive targets for bad actors. If you use a platform to buy, sell, or hold bitcoin or other digital assets, take extra care with your password, sign-in methods, email account, device, and withdrawal settings.
Different types of 2-Factor Authentication
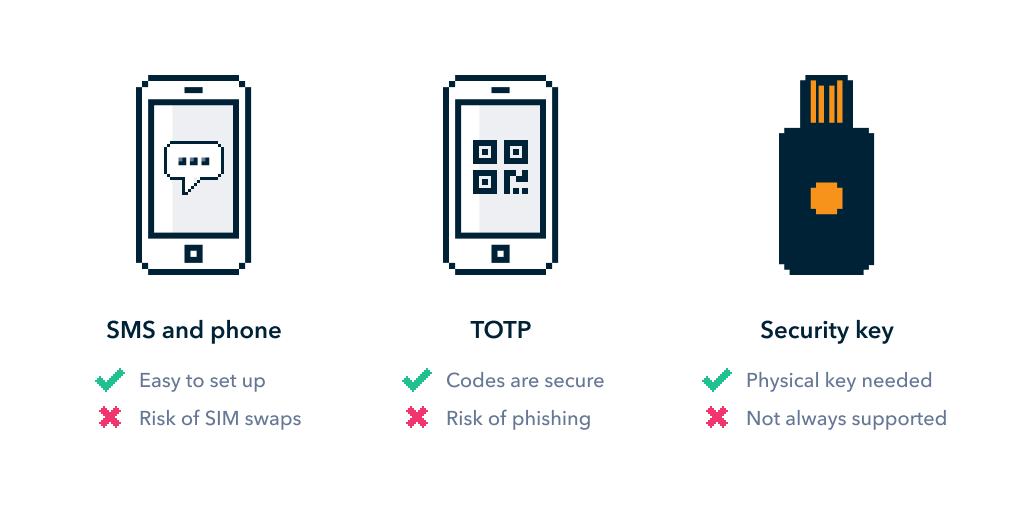
There are several ways to add another layer of account security. Each option has different trade-offs. In general, passkeys and FIDO security keys provide stronger protection against phishing than codes you manually type. Authenticator apps are usually stronger than SMS, while SMS may still be better than using a password alone when no stronger option is available.
SMS and phone verification
SMS and voice verification are easy to set up and remain the only option for some accounts. They are more vulnerable than authenticator apps, passkeys, and security keys because phone numbers can be targeted through SIM-swap attacks.
If an attacker takes control of your phone number, they may receive sign-in or account-recovery codes sent by text. SMS codes can also be captured through phishing if you enter them into a fake login page.
Use a stronger option when one is available. If SMS is the only option, use it rather than relying on a password alone—and never share an SMS code with anyone.
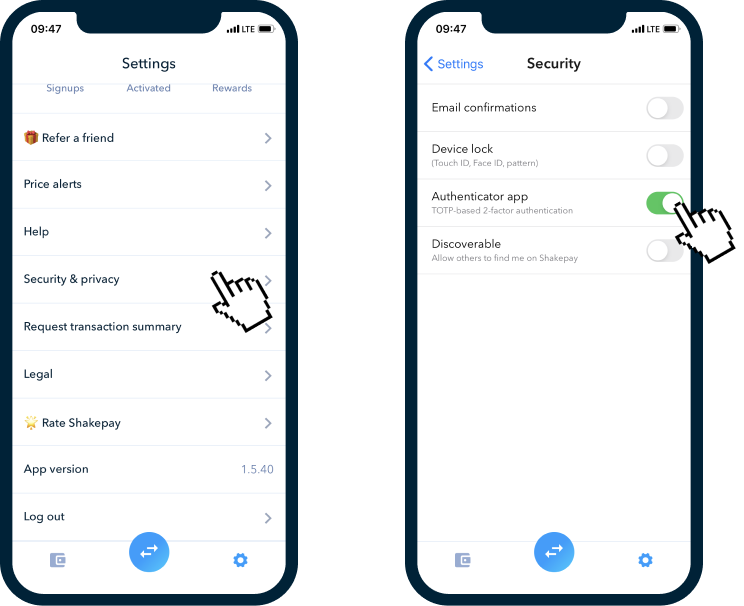
For Shakepay, SMS-based 2FA is enabled by default. Shakepay recommends upgrading to TOTP with an authenticator app.
2FA with authenticator apps
Authenticator apps are generally a stronger option than SMS. One common method is Time-based One-Time Passwords, or TOTP. A TOTP authenticator app creates a temporary code that you enter after your password when you sign in. You can use an authenticator app such as Google Authenticator or Microsoft Authenticator. Like with SMS verification, services will ask for your TOTP verification code after you’ve entered your username and password.
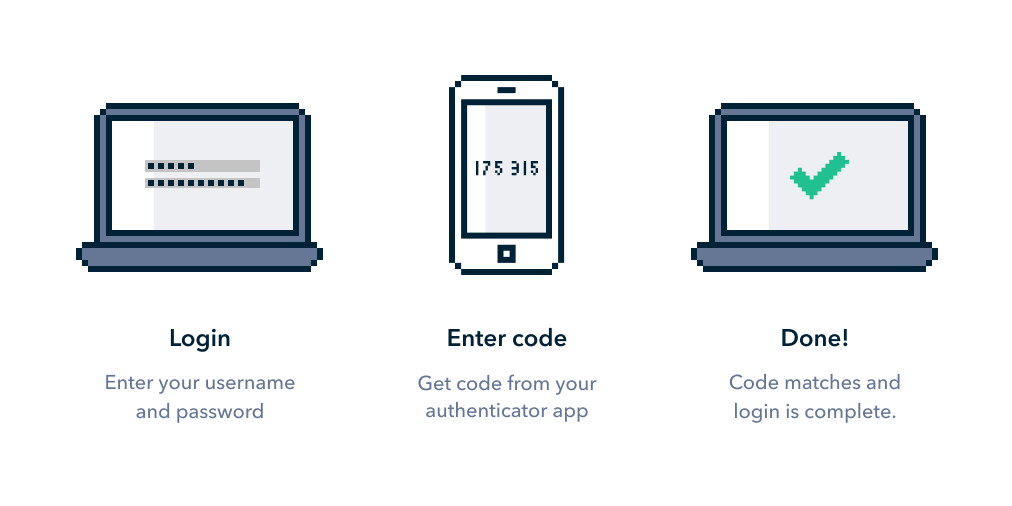
The difference here is that TOTP 2FA doesn’t require you to trust your mobile phone carrier for your account security (that is, assuming you have removed SMS verification and SMS recovery from your account).
Setting up TOTP 2FA with your accounts
To set up TOTP 2FA, you will have to use Google Authenticator to scan a QR code or enter a 2FA seed (a string of letters and numbers) that has been securely transmitted to you by the service.
Your authenticator app uses this code to generate unique numbers. These codes typically change every 30 seconds. Having the right numbers at any particular time tells the online service you have the device where the 2FA seed was installed, making it count as “something you have.”
When prompted, you look up the numbers generated in Google Authenticator and type them into the website’s login page to finish logging in.
Be careful, TOTP is still susceptible to phishing attacks
The main drawback of TOTP 2FA is that you can still be fooled into giving away your TOTP verification code in a phishing attack.
A phishing attack will trick someone into giving away their login credentials with a fake website that looks almost exactly like the login page to a service they use.
Quick phishing demo. Would you fall for something like this? pic.twitter.com/phONMKHBle
— Mustafa Al-Bassam (@musalbas) September 9, 2018
Would you fall for this phishing email?
How phishing attacks happen
- A hacker presents you with a link to a fake login page for your service, usually in the form of a fake email or a fake ad. (Often the only way to spot these fake websites is to check its URL)
- Once you enter your login credentials on this phishing page, the hacker’s automated system will grab the login credentials you type in, including your username, password, and 2FA code.
- The hacker’s computer will then quickly log into your account on their behalf.
- The hacker now has full access to your account as if you had logged in on their computer.
- The hacker will then change your password and 2FA codes, locking you out of your own account.
A TOTP code proves that you have access to your authenticator app. It does not prove that the website asking for the code is legitimate. Always open the official app or website yourself, check the URL carefully, and never share a code with someone who contacts you unexpectedly.
What about backups?
Before enabling TOTP, check how the service handles account recovery. If it provides one-time recovery codes, store them somewhere secure and private. Treat them like passwords.
If you choose to back up a TOTP setup secret, don’t leave an unprotected screenshot in your photo library, cloud storage, email, or shared notes. Use a secure offline location or a reputable encrypted backup method, depending on the service and your own security setup.
Keep your recovery information separate from the device you use to sign in when possible. Make sure you understand the recovery process before you need it, and don’t assume that every service offers the same recovery options.
Should I use my password manager for 2FA?
Password managers like 1Password also give you the option to store your TOTP 2FA seeds in your password database so that it can act as your authenticator app.
The advantage of this is that they can generate and automatically fill in the numerical code from in your browser. These 2FA codes will also be backed up across your devices.
For everyday accounts, this convenience may be reasonable when your password manager is protected with a strong, unique password and an additional sign-in method. For your most sensitive accounts, consider using a passkey or FIDO security key, or a separate authenticator app with a carefully protected recovery method.
Passkeys and FIDO security keys
Passkeys and FIDO security keys use cryptographic credentials instead of codes that you manually type. They are designed to bind the sign-in to the legitimate website or service, which makes them much harder for a fake website to use.
A passkey is usually stored on a phone, computer, password manager, or security key. To use it, you may approve the sign-in with Face ID, another biometric, or a device PIN. Passkeys can also allow you to remove your account password after setup, depending on the service. Learn how to set up a passkey on your Shakepay account.
A FIDO security key is a physical device that you register with an account. When you sign in, you connect or tap the key and approve the request. Some security keys work with phones through NFC, while others connect through USB or another supported method.
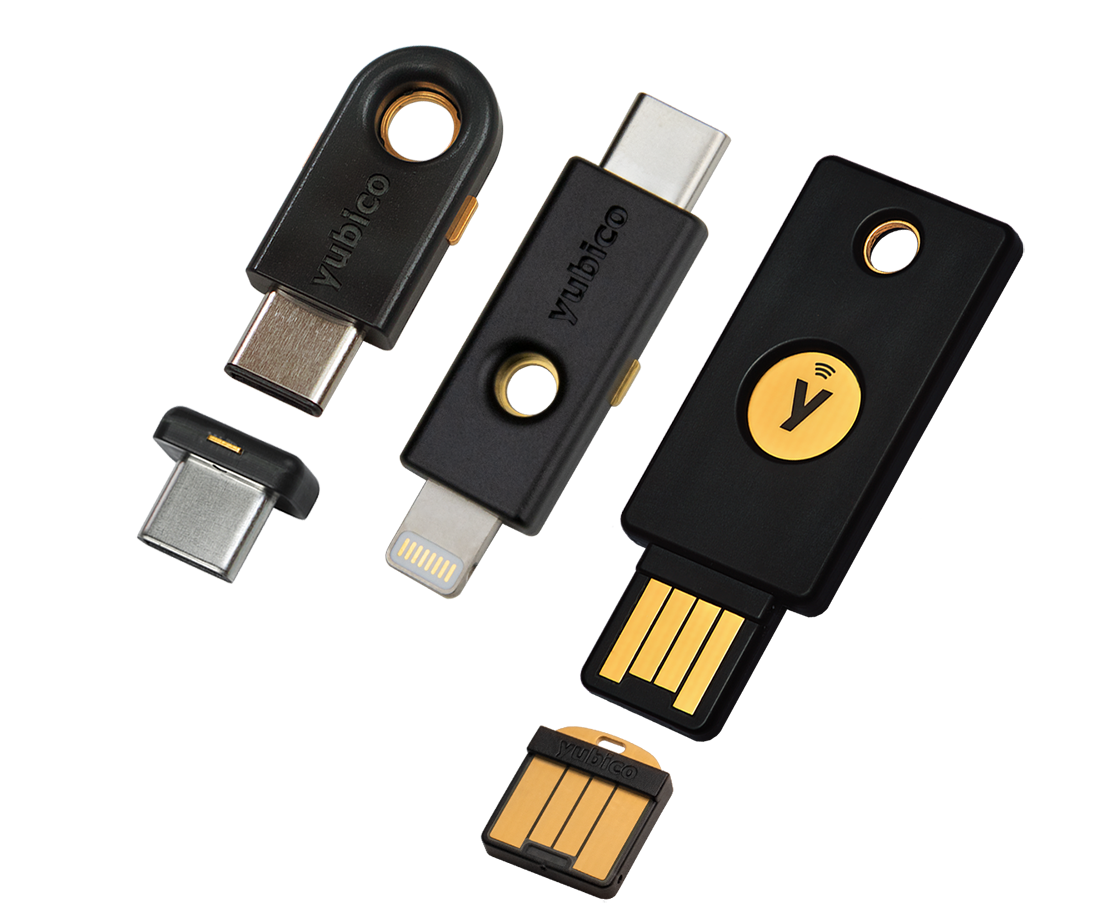
Passkeys and FIDO security keys are strong options for accounts that support them because the credential is tied to the intended service. A fake website generally cannot use the credential to sign in to the real account.
No sign-in method removes every risk. Protect your devices, keep your recovery options secure, and register a backup passkey or security key when the service allows it.
Lock down your most important accounts
Start with accounts that can reset other accounts, such as your primary email address, password manager, financial accounts, and digital-asset platforms.
Choose a passkey or FIDO security key when the account supports one. Otherwise, use an authenticator app. Review your account-recovery options so they are secure, available when you need them, and not easier to compromise than your primary sign-in method.
Which security key should I choose?
Choose a FIDO security key that is supported by the account and the devices you use. Check whether it supports USB, NFC, or another connection that works for you.
Consider registering a second key and storing it in a secure location in case your primary key is lost or damaged.
Securing your Shakepay account today
All Shakepay accounts are protected with 2FA. SMS-based 2FA is enabled by default, and we recommend upgrading to TOTP with an authenticator app.
You can also enable passkeys for your account. In the Shakepay app, go to Settings → Security & privacy → Passkeys. Passkeys use your device’s biometrics or PIN and even allow you to remove your password after setup.
Shakepay also offers other account-protection features, including device lock, email confirmations for crypto withdrawals, and account notifications. For current options and setup instructions, see Shakepay’s account-security guide and Security page.
Our 2FA recommendations
The best option depends on what the account supports:
- Use a passkey or FIDO security key when available.
- Otherwise, use an authenticator app rather than SMS when possible.
- Use SMS when it is the only available option, but remember that it is more vulnerable to SIM swaps.
- Protect recovery codes and TOTP setup secrets.
- Never share a password, verification code, or passkey approval.
- Use only the official app or website to sign in.
- Turn on account notifications and withdrawal confirmations when available.
- Pause when a message creates urgency or asks you to move money or bitcoin.
- Contact the service through an official support channel if something feels wrong.
Thanks for reading
We hope this has been a helpful, clear, and thorough guide on 2-Factor Authentication and how to make use of it in setting up your online accounts.
Good account security isn’t about finding one perfect tool. It’s about using a strong sign-in method, protecting your recovery options, keeping your devices secure, and slowing down when a message asks for sensitive information.
Further reading
How to enable 2FA with an authenticator app